Koshkenbek Dauren
Cybersecurity Specialist · SOC Analyst L1
Open to work · Astana, Kazakhstan
Experience SOC Analyst L1 · Blue Team — Sauyt Lab, Sr Holding
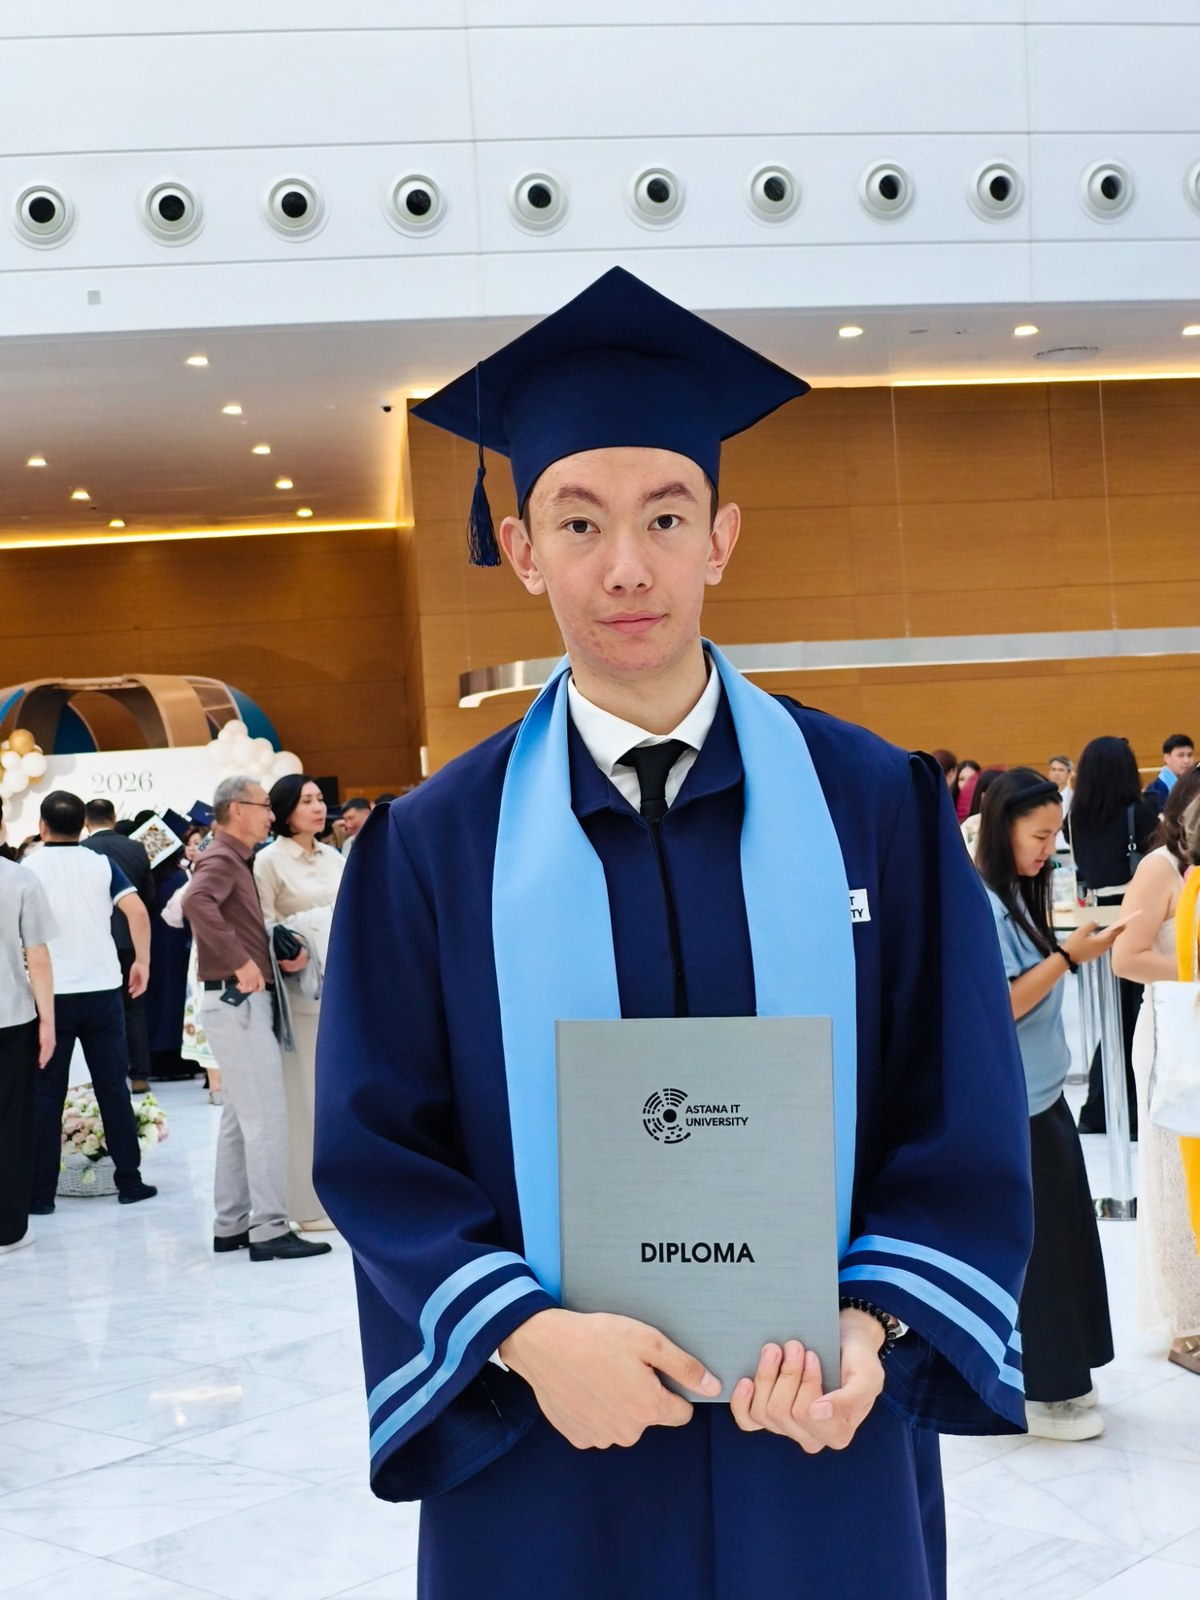
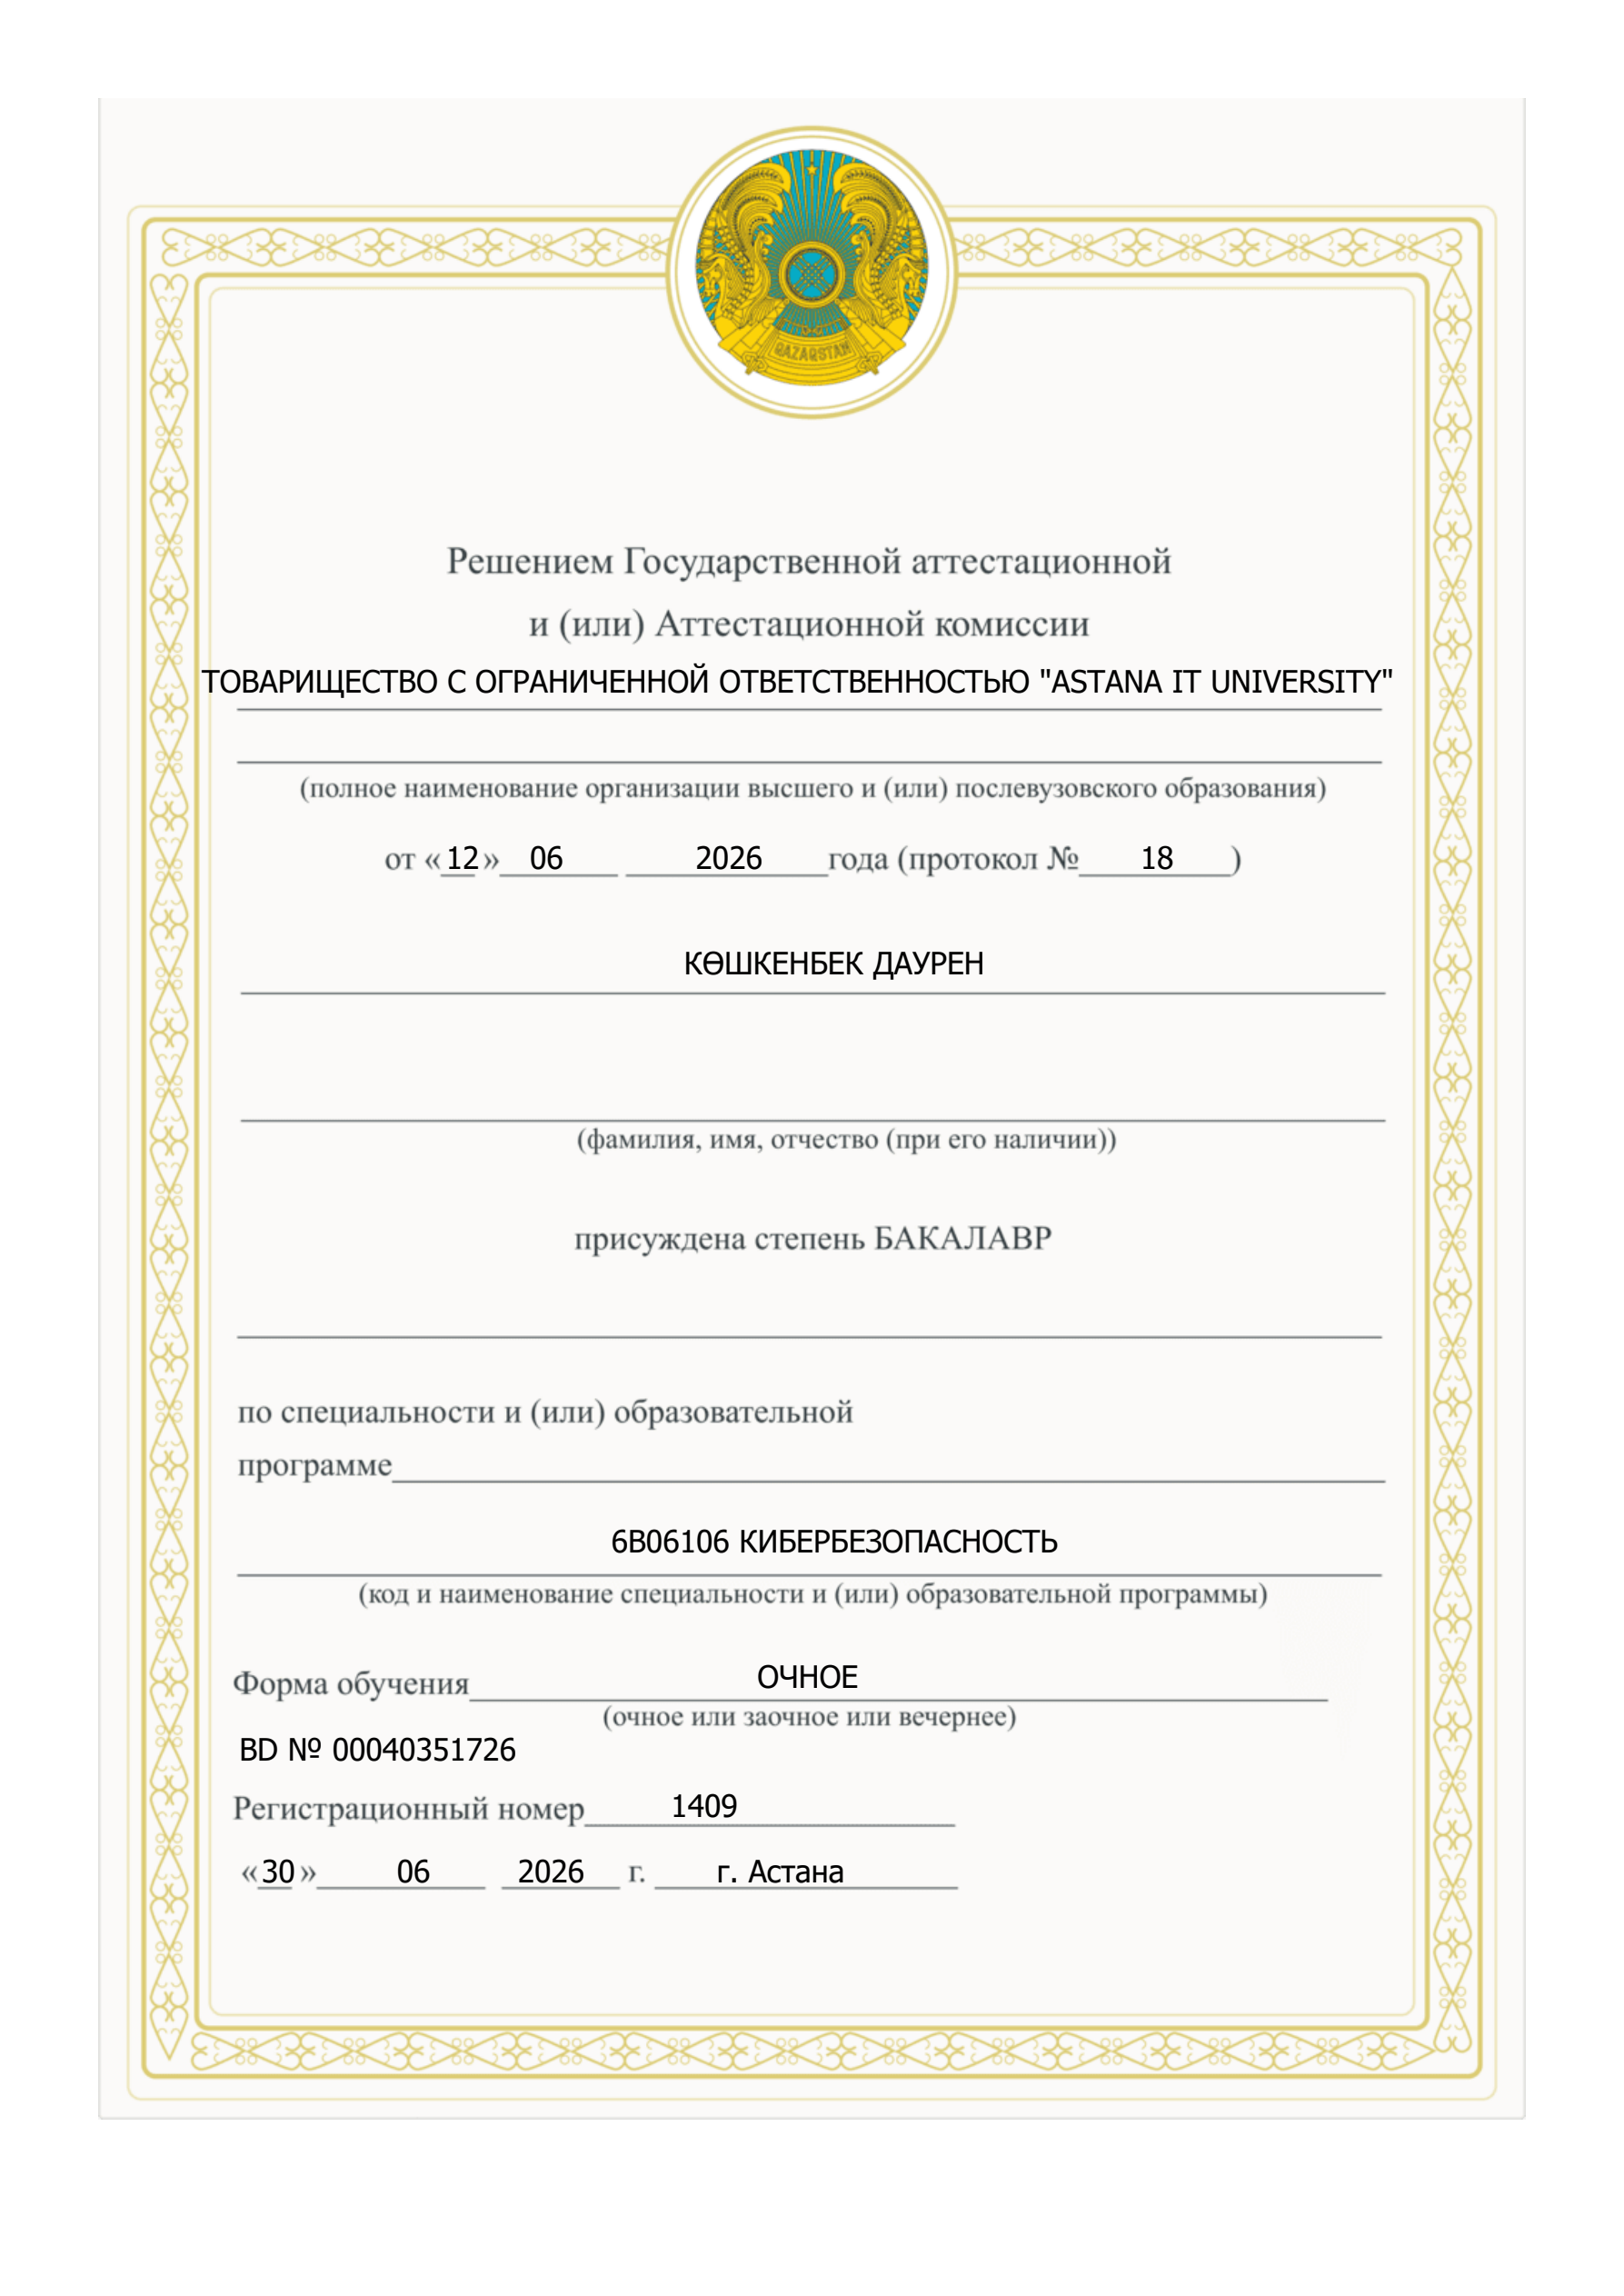
Education Astana IT University — Cybersecurity (graduated 2026)
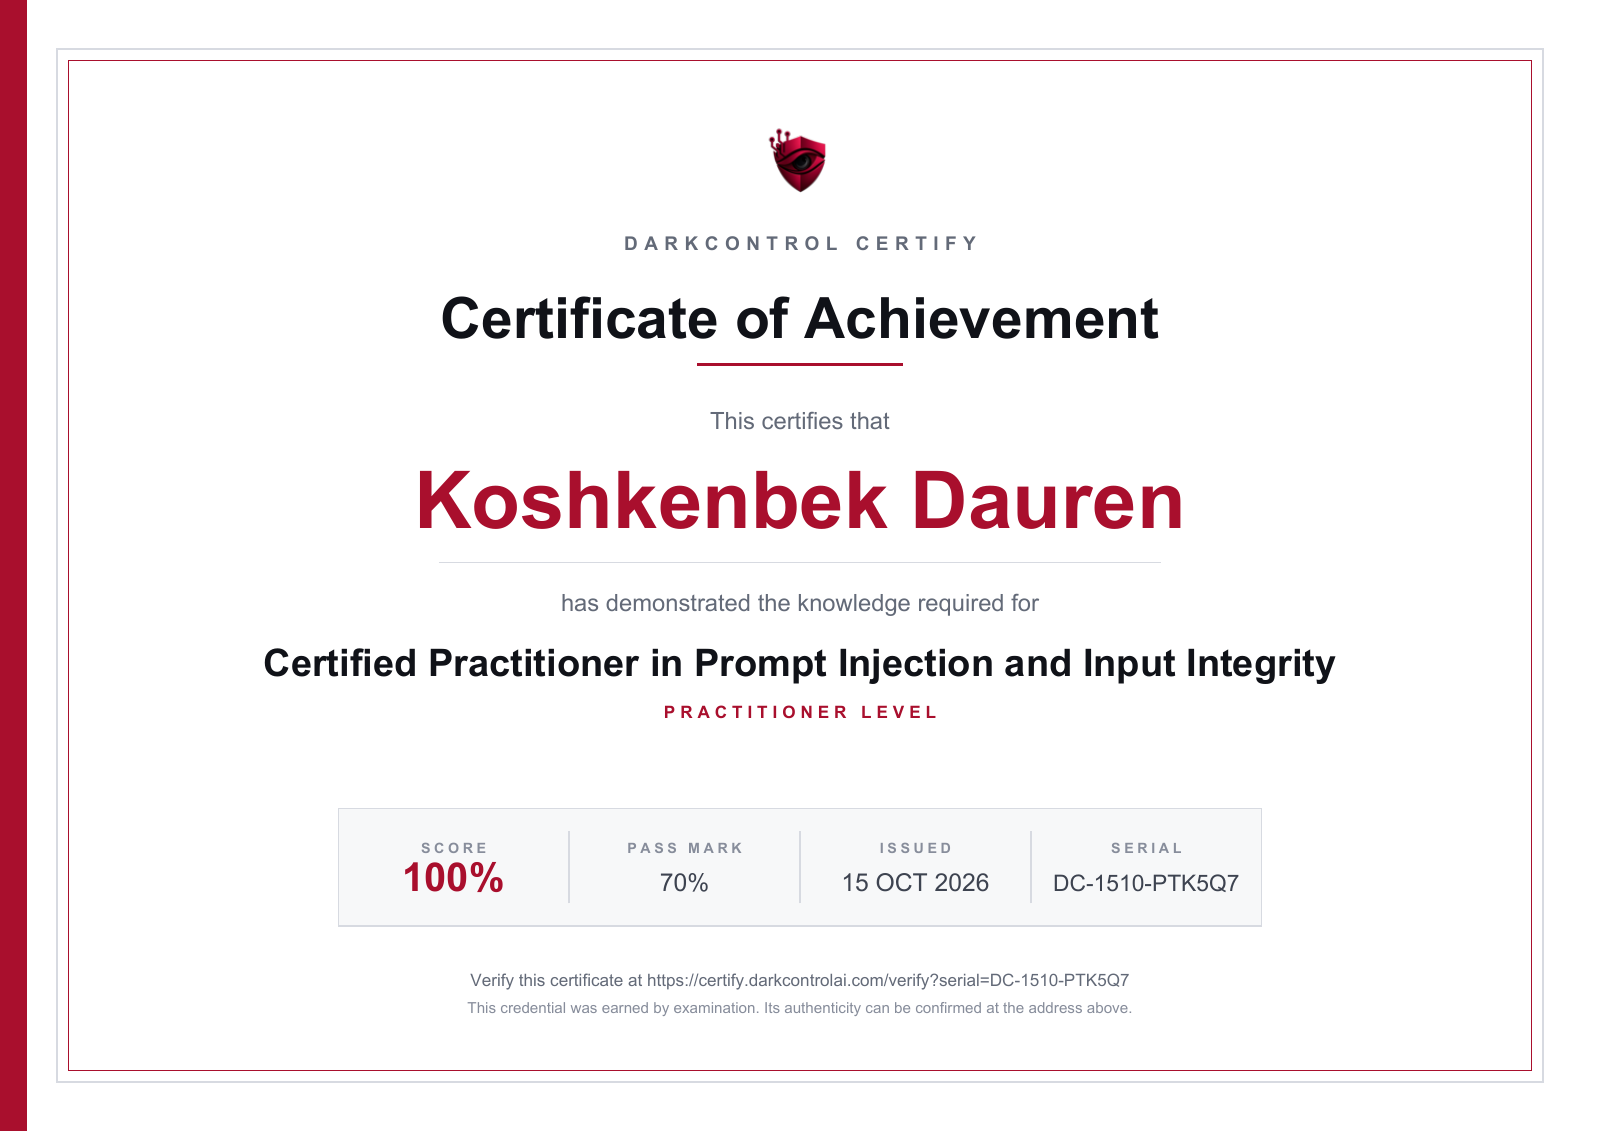
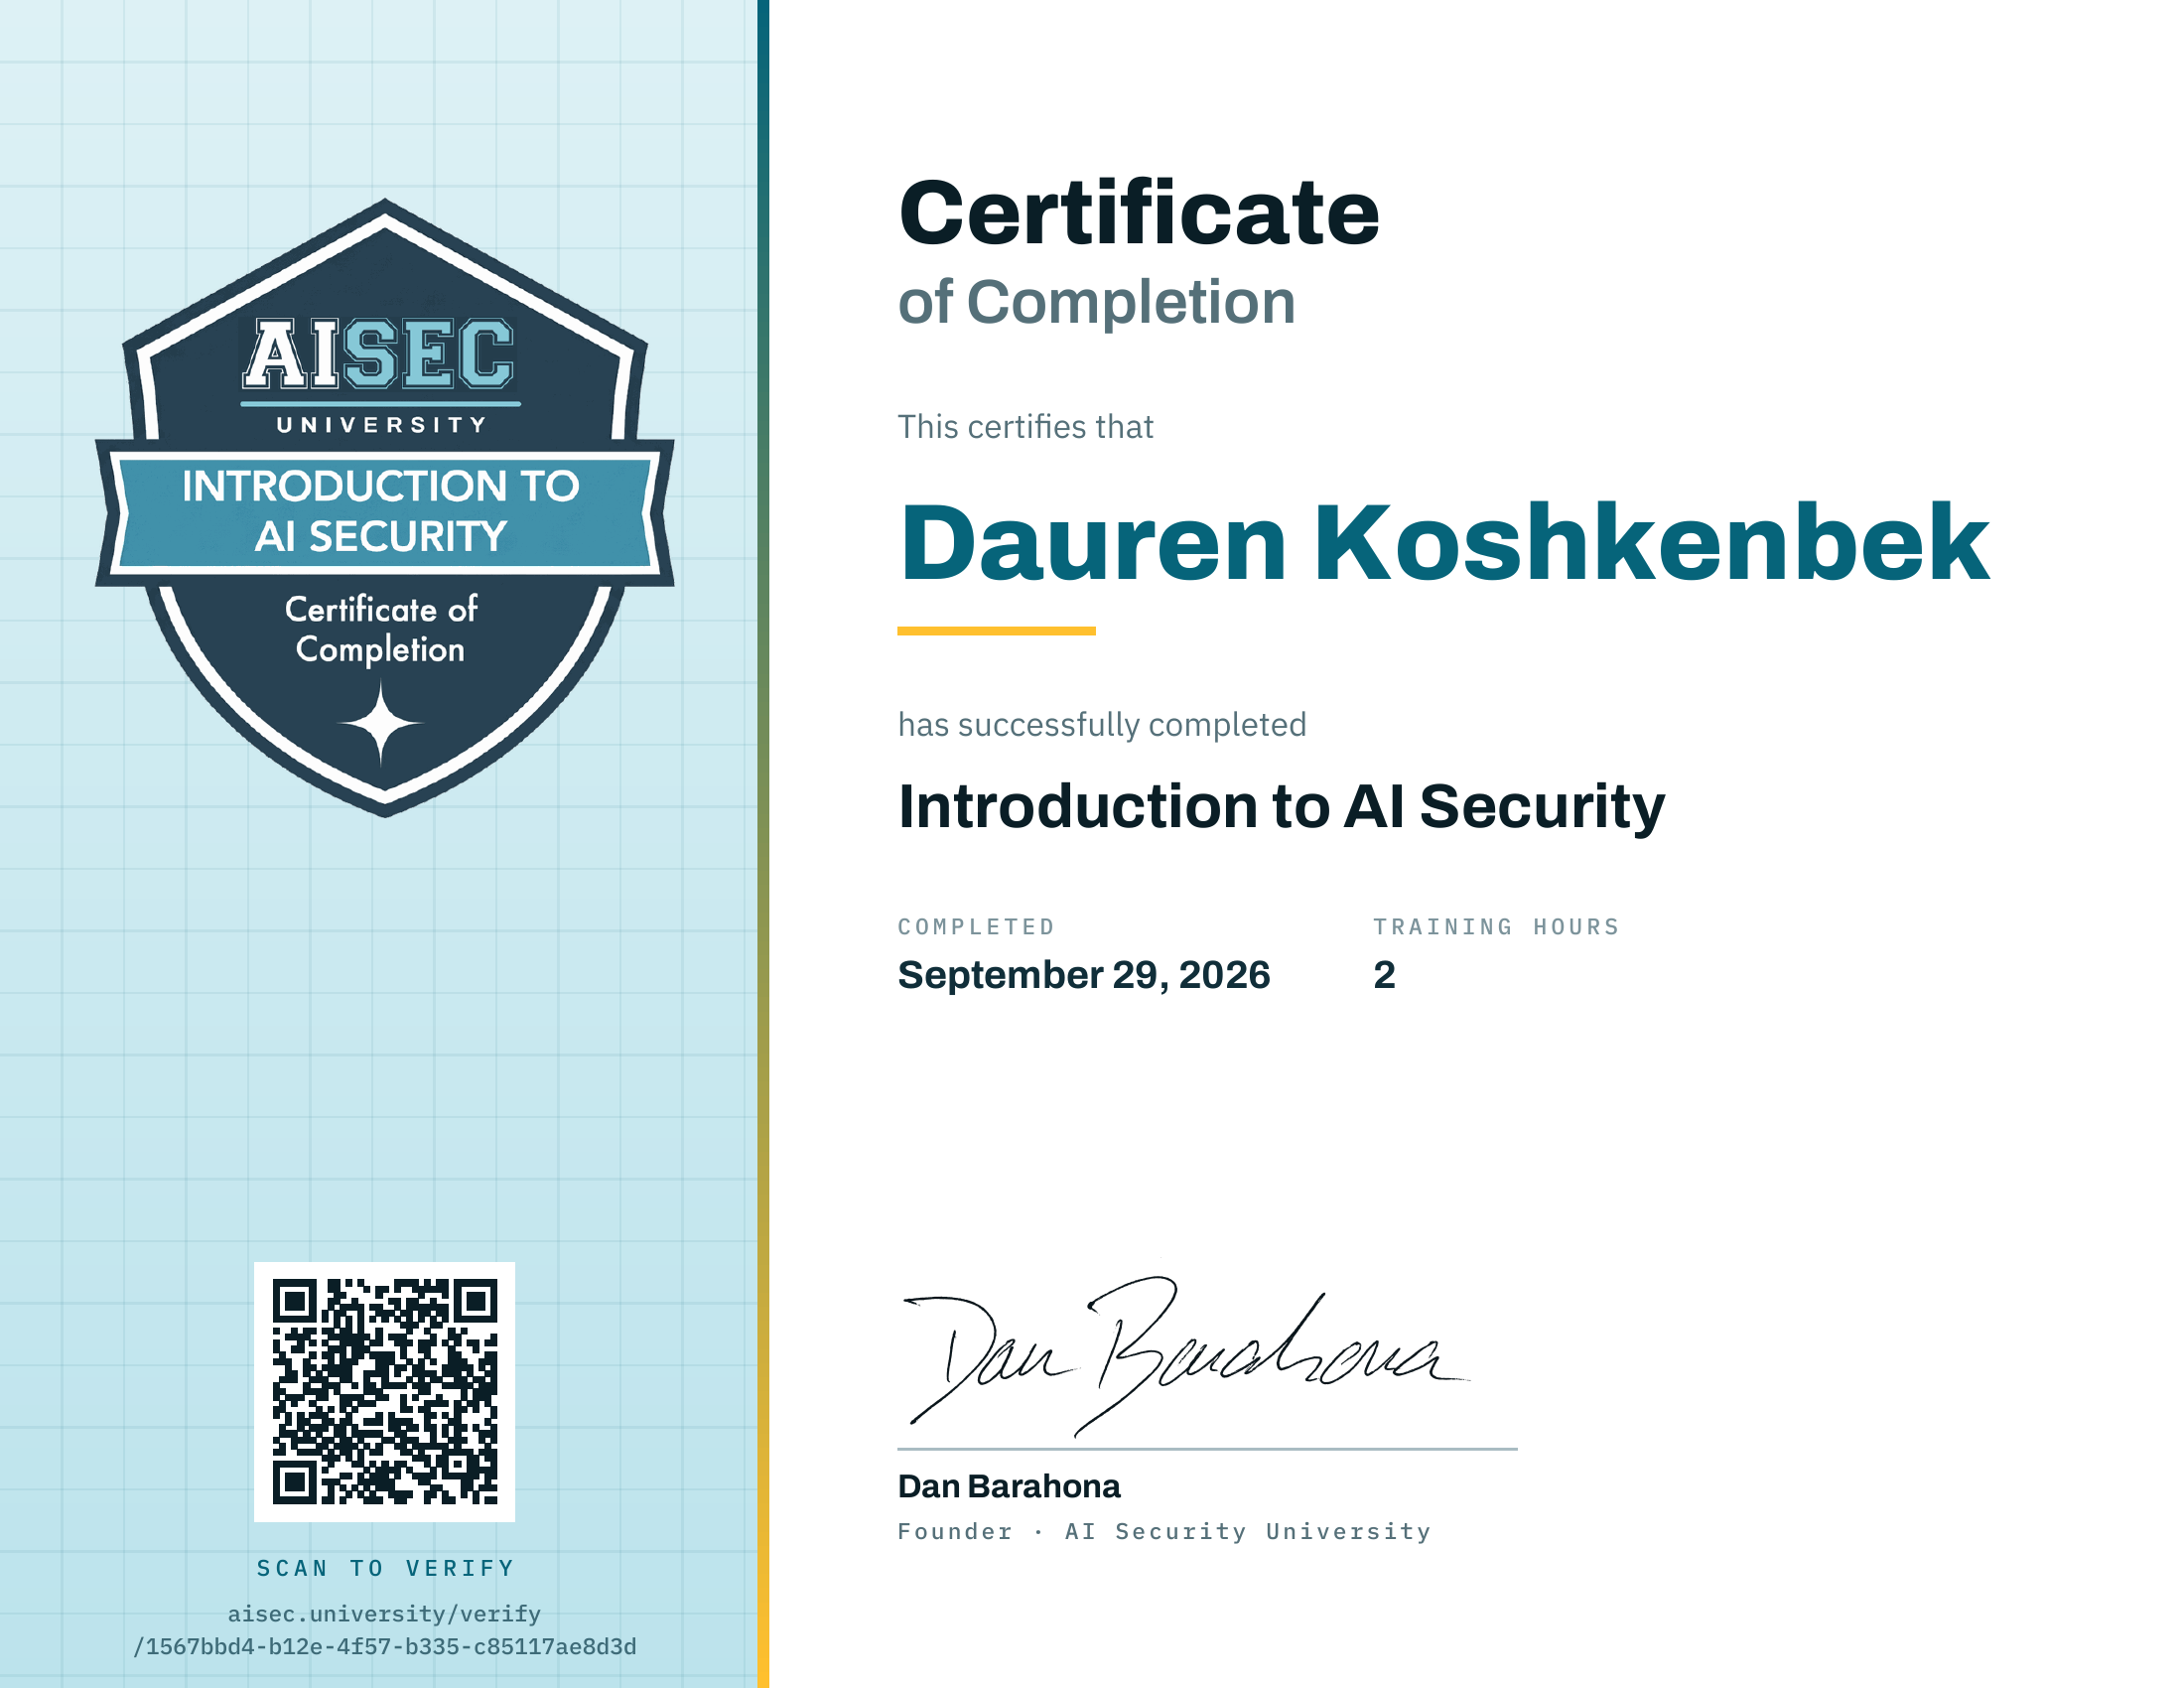
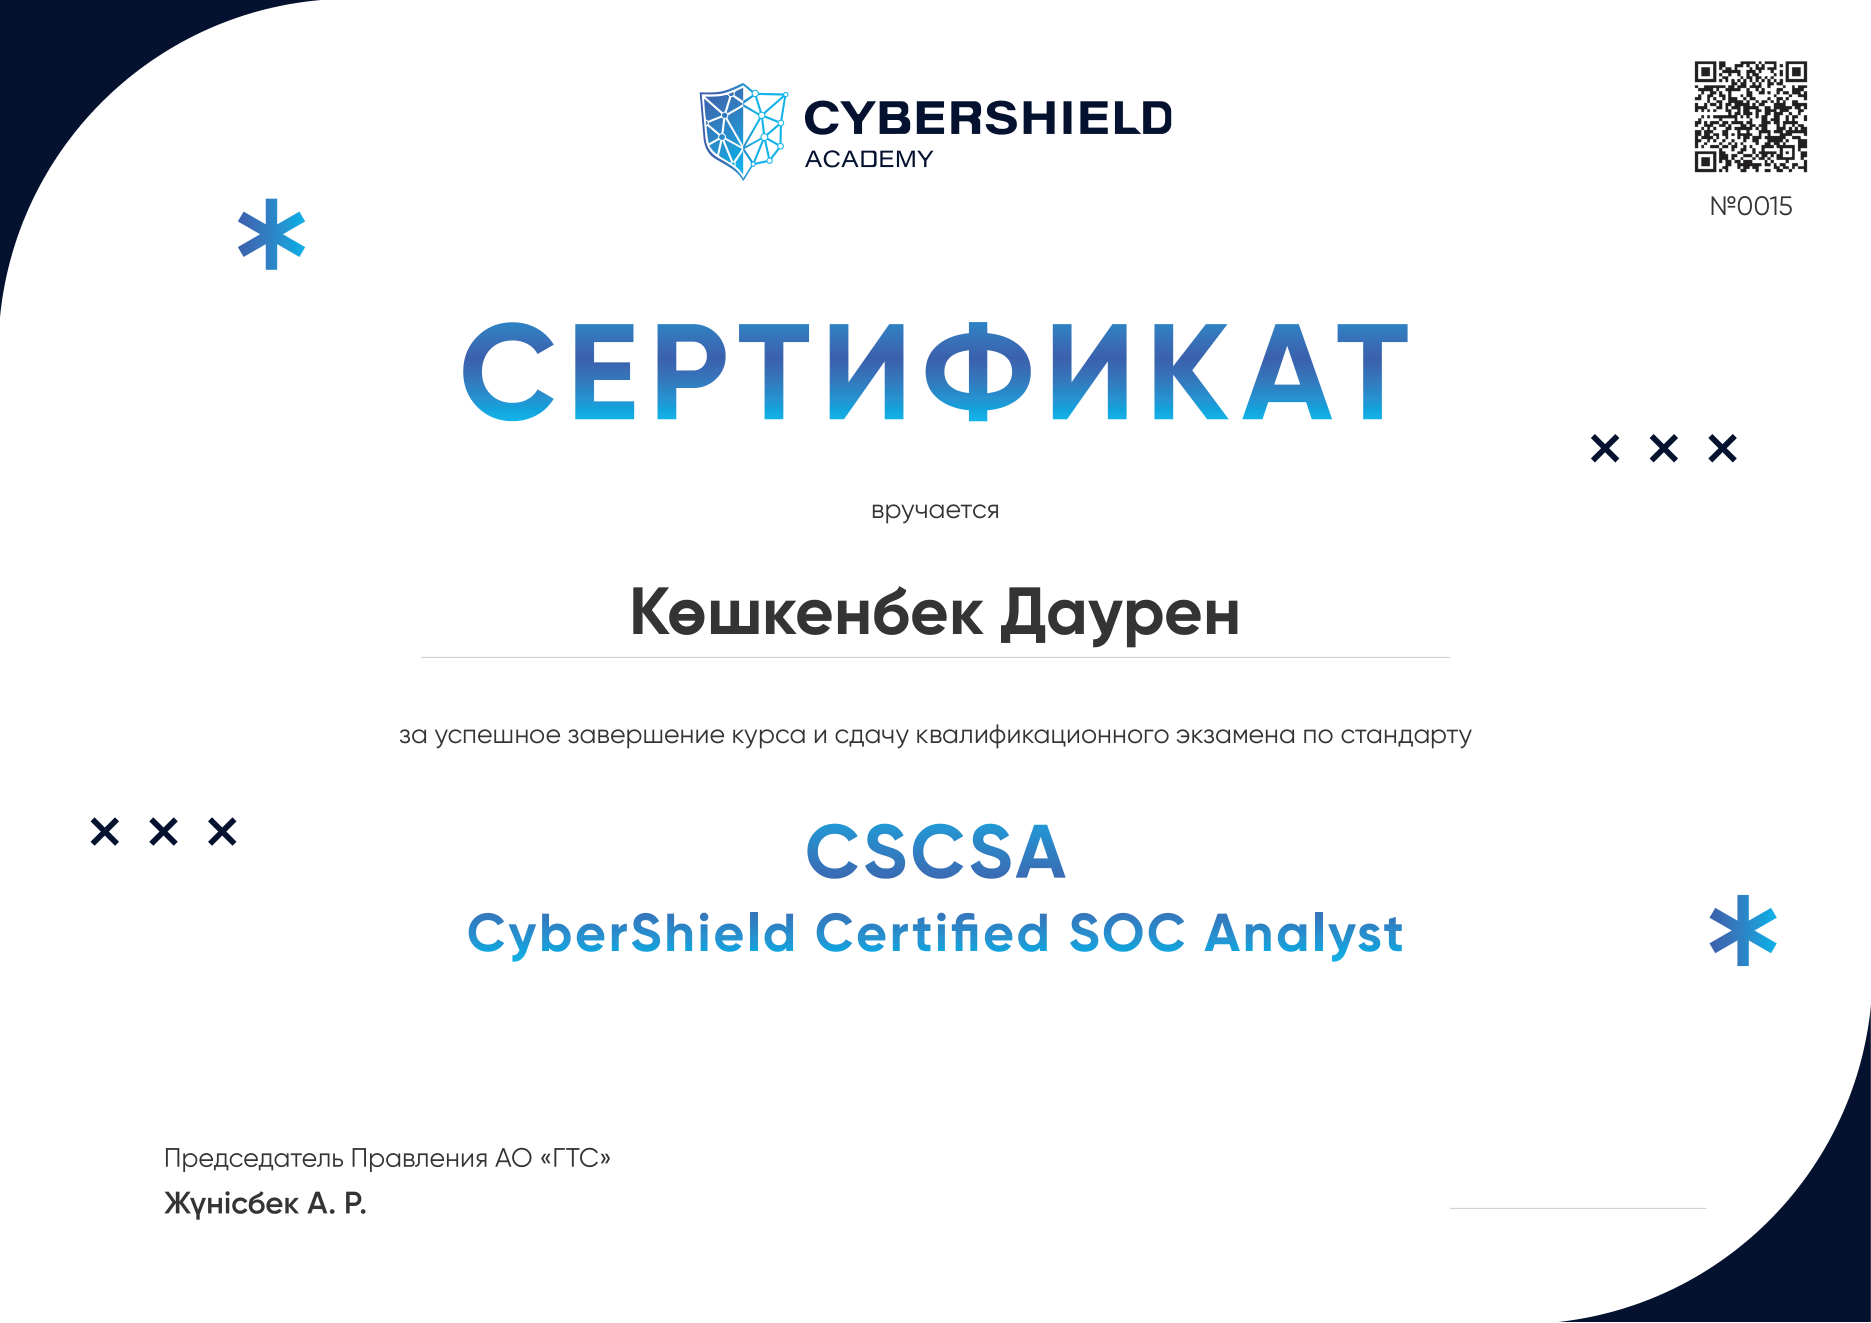
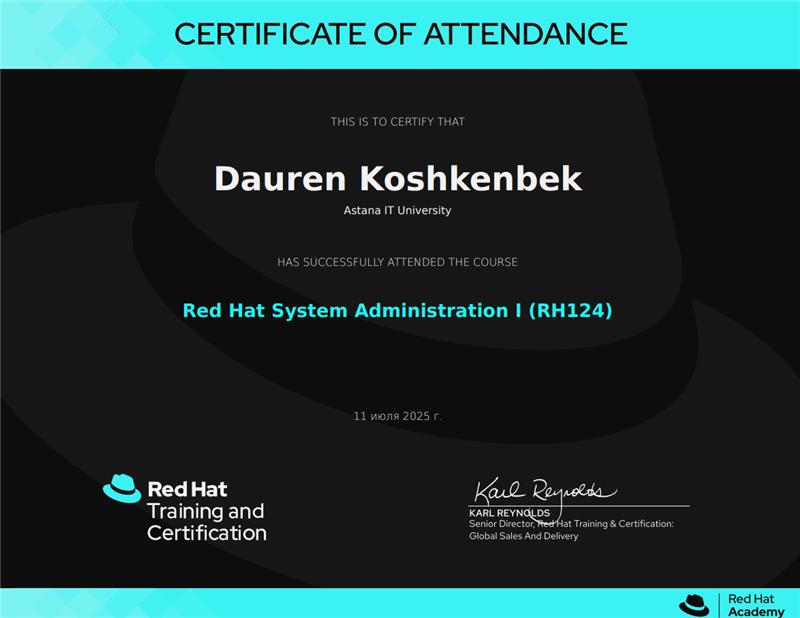
Certifications & Training DarkControl Prompt Injection · AI Security University · CyberShield CSCSA · Red Hat RH124 attendance
Languages Kazakh · Russian C1 · English B1 · Chinese HSK5
WHOAMI
DAUREN KOSHKENBEK SOC ANALYST L1 / PENTESTER (IN TRAINING)
I'm a cybersecurity specialist focused on security monitoring, incident analysis and offensive security. I enjoy turning complex security data into clear insights and building practical solutions.
CV
EN
RU
KZ
KOSHKENBEK D. SOC L1 · ASTANA, KZ
ACCESS GRANTED
HACK
BLUE + RED
▸ 08:21 Suspicious login attempt 203.0.113.18 ▸ 08:17 PowerShell execution endpoint-04 ▸ 08:12 Port scan detected 198.51.100.7 ▸ 08:10 Web shell upload /wp-admin/
SIEM Monitoring 85%
Log Analysis 85%
Threat Analysis 65%
Incident Response 70%
Self-assessed proficiency, not telemetry.
// BLUE TEAM DETECT / ANALYZE / RESPOND
Security monitoring (SIEM)
Log analysis & incident investigation
Threat analysis
Security reporting
// RED TEAM FIND / EXPLOIT / VALIDATE
Reconnaissance & enumeration
Web application testing
Network & infrastructure testing
Privilege escalation
IN TRAINING
Offensive Security
Kali
Burp
Metasploit
Nmap
SQLMap
Development
Python
React
TypeScript
Docker
Git
Prompt Injection & Input Integrity DarkControl Certify · 15 Oct 2026
Introduction to AI Security AI Security University · 29 Sep 2026 · 2 hours
CyberShield CSCSA CyberShield Academy · State Technical Service (STS)
Red Hat RH124 Red Hat Training and Certification · 11 Jul 2025
Bachelor's — Cybersecurity Astana IT University · 2026
Security is not a product, but a process. — Bruce Schneier
01
02
03
04
05
06
I am Koshkenbek Dauren, a Cybersecurity graduate of Astana IT University and a SOC Analyst L1.
SHORT-TERM GOAL SOC Analyst L2 / Blue Team Engineer
LONG-TERM GOAL Penetration Tester with strong defensive background
OFFENSIVE SECURITY Web Pentesting Network Security Vulnerability Research DEFENSIVE SECURITY SOC Monitoring Log Analysis Incident Response DEVELOPMENT Web Applications Security Tools Automation RESEARCH Threat Analysis Security Education New Technologies
Kazakh — Native Russian — C1 English — B1 Chinese — HSK 5
BLUE TEAM MINDSET I focus on visibility, detection logic, and understanding what is normal versus suspicious behavior in systems and networks.
RED TEAM MINDSET I analyze systems from an attacker’s perspective, looking for misconfigurations, weak points, and realistic attack paths.
SOC Analyst L1 Sauyt Lab (Freedom)
February 03, 2026 – Present
Security event monitoring in SOC environment
Log analysis from network, endpoint, and system sources
Initial alert triage and incident investigation
Identification of suspicious activity and escalation
Working within a high-responsibility national security environment
SOC Analyst L1 Sr Holding (China)
September 01, 2025 – February 01, 2026
Security event monitoring in SOC environment
Log analysis from network, endpoint, and system sources
Initial incident triage and alert investigation
Identification of suspicious activity and escalation when required
Working with security monitoring tools and dashboards
Network Security Project Participant Kazakhtelecom (Sapa+)
January 20, 2025 – June 20, 2025
Participation in a network security project
Support of secure network infrastructure
Monitoring and basic analysis of network security events
Working within a large enterprise telecom environment
PROJECTS REAL PROJECTS. REAL IMPACT.
INTERACTIVE SIMULATION
GHOST PACKET
Intercept three rogue packets as they race through a simulated network.
PLAY SIGNAL HUNT
ATTACK CHAIN & SKILLS TOOLS. MINDSET. RESULTS.
02 ENUMERATION Burp Suite Nuclei Gobuster Nikto 03 EXPLOITATION Metasploit SQLMap Custom Scripts 04 PRIVILEGE ESCALATION Linux Windows BloodHound PowerShell 05 POST-EXPLOITATION Lateral Movement Persistence Data Extraction 06 REPORTING Documentation Risk Analysis Recommendations
The offensive part of this chain is what I am training toward; the defensive side is what I do at work.
Kali Linux
Burp Suite
Metasploit
Nmap
SQLMap
Python
React
TypeScript
Next.js
Supabase
Docker
Git
CREDENTIAL VAULT CREDENTIALS & TRAINING
Astana IT University Bachelor’s Degree — Cybersecurity
Graduated in 2026
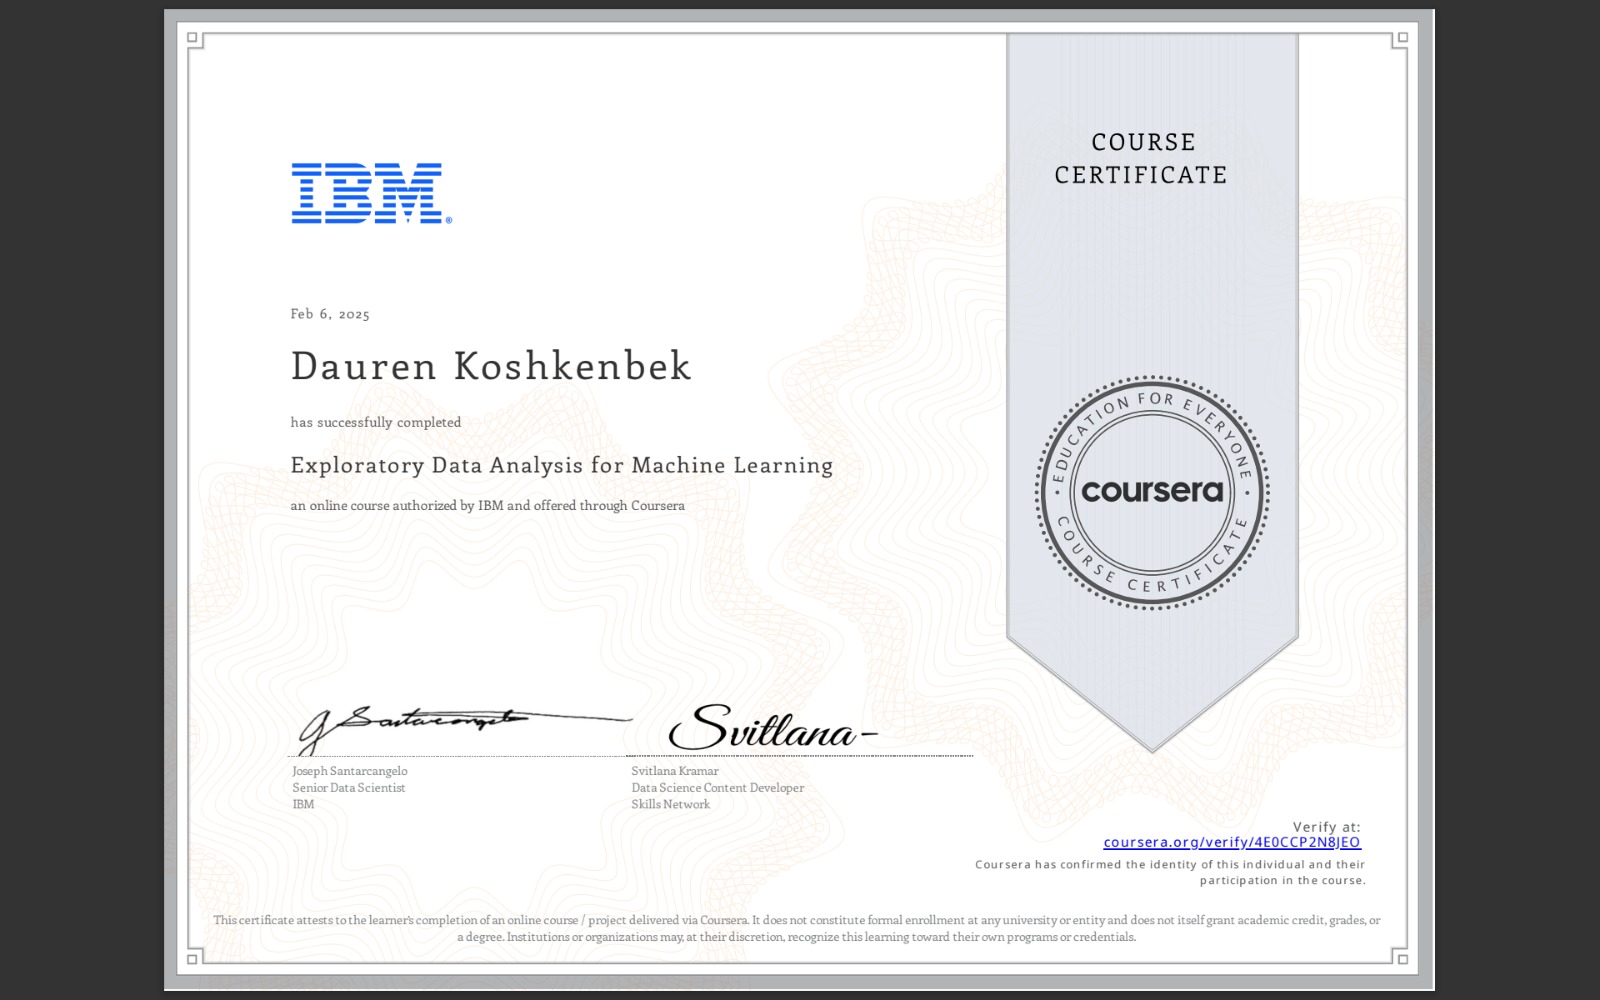
Exploratory Data Analysis for Machine Learning IBM • ID: 4E0CCP2N8JEO
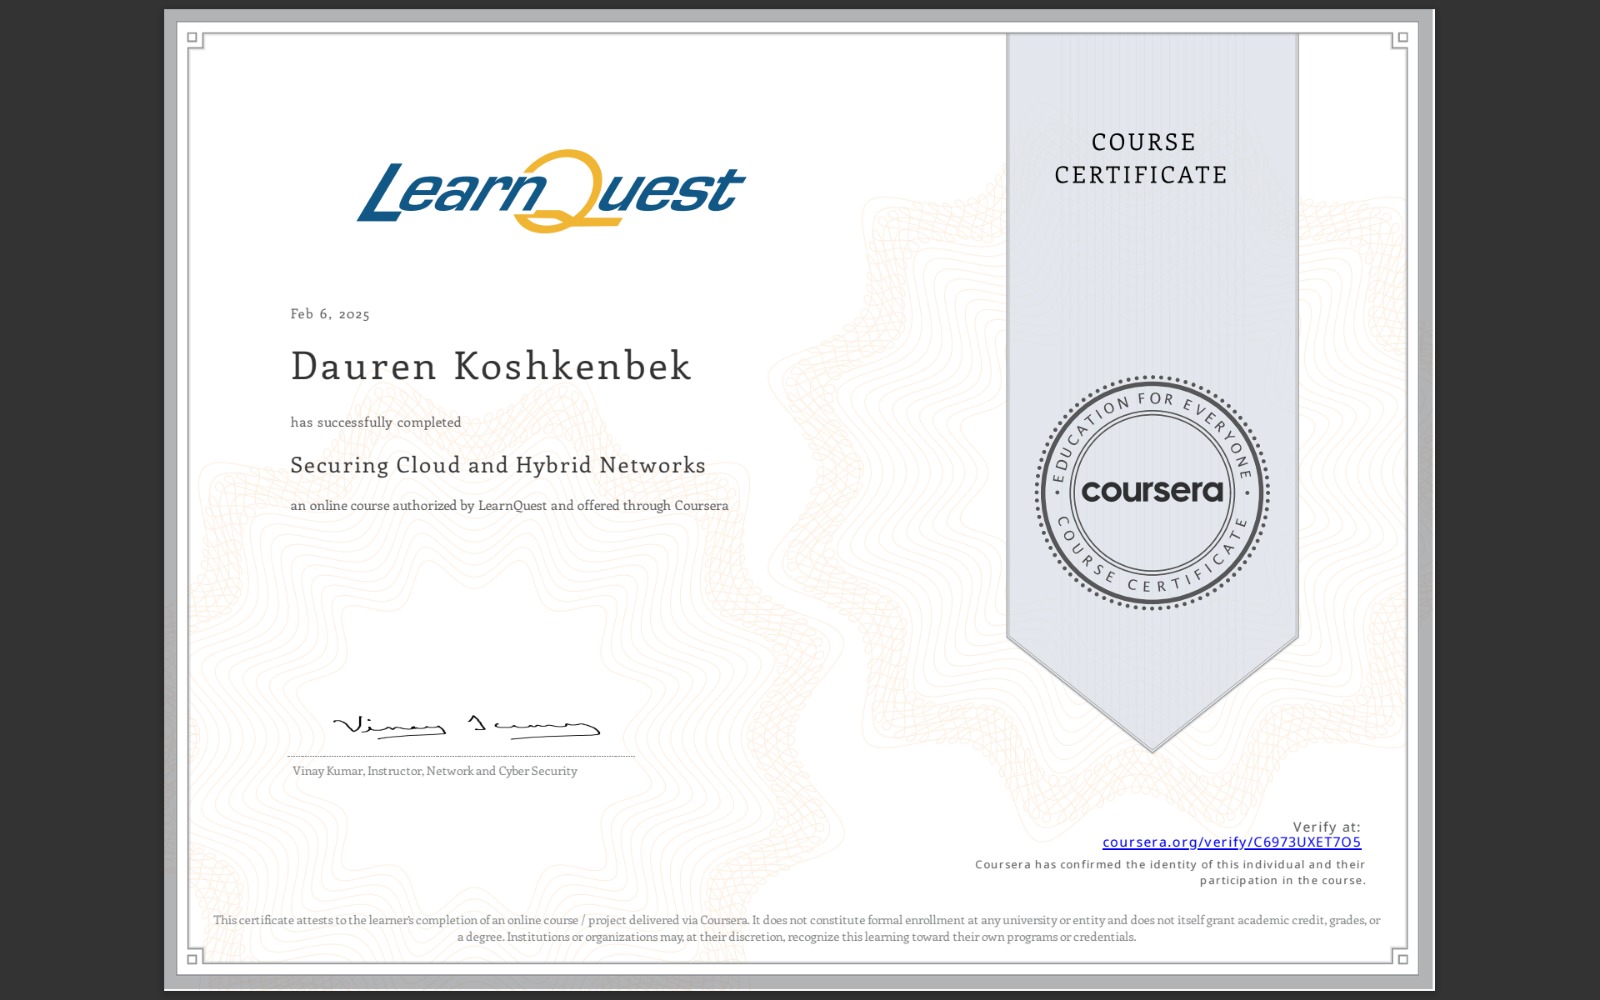
Securing Cloud and Hybrid Networks LearnQuest • ID: C6973UXET7O5
Next-Generation Firewalls and Intrusion Prevention LearnQuest • ID: UVZK33SZYZ2E
Supervised Machine Learning: Regression IBM • ID: WGFI25H8VBDH